

This 312-50 certification practice guide is the best dump to me so far. It has details and is updated to the latest. I passed the exam in less than one hour.
 Matt


Exam Code: 312-50
Exam Name: Certified Ethical Hacker v13
Updated: Oct 09, 2026
Q & A: 923 Questions and Answers
312-50 Free Demo download
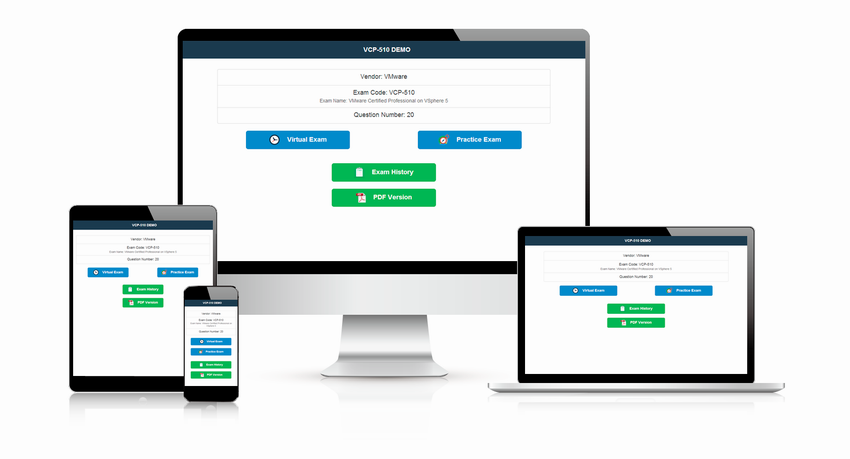
Everything you need for the 312-50 exam, in one place. Pass4cram's bank offers 923 expert-verified practice questions covering the EC-COUNCIL Certified Ethical Hacker v13 objectives — built by professional IT experts and certified trainers, updated constantly through 2026.
| Section | Weight | Objectives |
|---|---|---|
| Sniffing | 5% | - Sniffing Concepts
|
| Information Gathering and Reconnaissance | 10% | - Footprinting Countermeasures - Footprinting Methodology
|
| Denial-of-Service | 5% | - DoS/DDoS Concepts
|
| Cloud Computing | 5% | - Cloud Computing Concepts
|
| Hacking Wireless Networks | 5% | - Wireless Countermeasures - Wireless Attack Techniques
|
| Session Hijacking | 5% | - Session Hijacking Countermeasures - Session Hijacking Concepts
|
| Malware Threats | 5% | - Malware Concepts
|
| Evading IDS, Firewalls, and Honeypots | 5% | - Countermeasures - Firewall Concepts
|
| Scanning Networks | 10% | - Scanning Methodology
- Network Scanning Concepts
|
| Hacking Mobile Platforms | 5% | - Mobile Attacks
|
| Cryptography | 5% | - Cryptography Concepts
- Public Key Infrastructure (PKI)
|
| Social Engineering | 5% | - Social Engineering Countermeasures - Social Engineering Concepts
|
| Hacking Web Servers | 5% | - Web Server Concepts
|
| Enumeration | 5% | - Enumeration Concepts
|
| Vulnerability Analysis | 5% | - Vulnerability Analysis Methodology - Vulnerability Assessment Concepts
|
| System Hacking | 10% | - System Hacking Methodology
|
| Hacking Web Applications | 10% | - Web Application Countermeasures - Web Application Concepts
- Web Application Attacks
|
| SQL Injection | 5% | - SQL Injection Concepts
|
At present, the 312-50 exam requires a passing score of 60-70% and costs $1,199 USD to register. EC-COUNCIL controls both figures, so confirm them on the official site before you book.
The latest exam information lists 125 questions for the 312-50 exam, to be completed in 240 minutes minutes. Rehearsing under these conditions in the online engine is the closest thing to sitting the real test.
The EC-COUNCIL Certified Ethical Hacker v13 blueprint is organized into these principal domains:
Additional domains follow in the full official outline, and our bank spans them all.
A team of professional IT experts and certified trainers who focus on this exam field — and who keep the 312-50 bank under constant updating so every candidate prepares smoothly. Every answer is expert-verified, and you can check the accuracy yourself with a free demo before buying. The online test engine deserves special mention: it simulates the actual test environment, supports Windows, Mac, Android, and iOS, carries no installation limits, and lets you practice without limits of time or location — a smooth preparation process for office workers who cannot attend classes.
Upon successful payment, our system automatically sends the product to your mailbox — typically within about a minute — with an instant download link on screen. If nothing arrives within two hours, check your spam folder and contact support. Once purchased, updates are free for 365 days: whenever a new version is released, the updated 312-50 bank is sent to your email immediately. A 50% renewal discount applies after the period ends.
EC-COUNCIL specifies the following prerequisites for the EC-COUNCIL Certified Ethical Hacker v13: At least 2 years of IT work experience recommended; completion of EC-Council official training or self-study accepted.
Verify the details on the official certification page before registering.
Documented and honored. If you fail the corresponding exam within 60 days of purchase, send a scanned copy of your enrollment slip and your official Score Report PDF within two days of the exam date; verified claims are refunded in full within seven days. Exclusions: exams taken within three days of purchase, candidate names that differ from the payer, and free or expired products. If you have another exam in mind, you can instead exchange your product for two others of equal value at no charge.
You are leading an internal red team assessment for a multinational bank with a highly complex and distributed IT infrastructure. Your team is required to simulate attacks across cloud services, servers, and remote endpoints. Due to the sheer scale of the environment, you deploy an AI-based platform that automatically scans the entire network, flags anomalies based on prior breach data, and adjusts its threat detection models as new attack behaviors are encountered.
What key benefit of AI-driven ethical hacking is most critical to your success in this scenario?
Correct Answer: C 🗳️
Explanation: Only visible for Pass4cram members. You can sign-up / login (it's free).
A tester evaluates a login form that builds SQL queries using unsanitized input. By submitting a single quote ('), the tester bypasses authentication and logs in. What type of SQL injection occurred?
Correct Answer: C 🗳️
Explanation: Only visible for Pass4cram members. You can sign-up / login (it's free).
During an internal audit at a financial services firm in Mumbai, ethical hacker Meera was tasked with assessing lateral movement risks within the Windows-based domain environment. While monitoring internal network traffic, she noticed a strange broadcast from a workstation trying to resolve a non-existent host. Suspecting protocol-level weakness, she responded swiftly using a pre-configured system. A few minutes later, she captured NTLMv2 hashes from several authenticated sessions across multiple departments. Later, her team successfully cracked one of the hashes offline and used the credentials to gain access to a sensitive internal reporting server. Which type of attack did Meera most likely execute?
Correct Answer: D 🗳️
Explanation: Only visible for Pass4cram members. You can sign-up / login (it's free).
An Nmap SMTP enumeration script returns valid usernames. What misconfiguration is being exploited?
Correct Answer: B 🗳️
Explanation: Only visible for Pass4cram members. You can sign-up / login (it's free).
During a penetration test at an e-commerce company in Boston, ethical hacker Sophia launches an HTTP flood against the checkout page of the site. The simulated traffic consists of repeated GET and POST requests designed to overload application-layer resources. In response, the IT team activates a security tool that inspects and filters malicious HTTP traffic while allowing legitimate customer requests to pass, ensuring service continuity during the exercise.
Which DoS/DDoS protection tool is most likely being used in this scenario?
Correct Answer: A 🗳️
Explanation: Only visible for Pass4cram members. You can sign-up / login (it's free).

Pass4cram confidently stands behind all its offerings by giving Unconditional "No help, Full refund" Guarantee. Since the time our operations started we have never seen people report failure in the 312-50 exam after using our products. With this feedback we can assure you of the benefits that you will get from our products and the high probability of clearing the EC-COUNCIL 312-50 exam.
We still understand the effort, time, and money you will invest in preparing for your certification exam, which makes failure in the 312-50 exam really painful and disappointing. Although we cannot reduce your pain and disappointment but we can certainly share with you the financial loss.
This means that if due to any reason you are not able to pass theactual 312-50 exam even after using our product, we will reimburse the full amount you spent on our products. you just need to mail us your score report along with your account information to address listed below within 7 days after your unqualified certificate came out.
Over 28240+ Satisfied Customers
This 312-50 certification practice guide is the best dump to me so far. It has details and is updated to the latest. I passed the exam in less than one hour.
Matt
It is really helpful to prepare for my exam with 312-50 dumps, I will choose it as only tool for my next exam.
 Patricia
I prepared 312-50 exam with Pass4cram real exam questions and passed it.
 Monroe

Good exam dumps. It is very useful for me. Thanks service Delia. very nice.
 Judith

The quantity of 312-50 practice question is the best. With the help of Pass4cram, I could prepare for the 312-50 exam in only one week and pass exam with high score.
 Katherine
If you are not well prepared for 312-50 exam and your exam date is coming nearer then join Pass4cram now for ultimate success.
 Stan
I cleared my 312-50 certification exam in the first attempt. All because of the latest exam dumps available at Pass4cram. Well explained pdf answers for the exam. Suggested to all candidates.
 Quintion
Today i passed the 312-50 exam. This Pass4cram dump is valid exactly. Read all of theory and then use this dump easily. Will purchase 312-38 products.
 Alva
Every certification exam means one step ahead in your career and I made progress in my career only with the help of Pass4cram 's study guide, dumps and practice tests. Hassle free solution to Ace Exam 312-50!
 Kirk
If you want to score great marks, you should try out the 312-50 practice test. Surely, you will pass the exam with good marks. I just did so.
 Kim
Great 312-50 practice questions from Pass4cram.
 Vivien
These 312-50 exam tests are real. Good for exam practice. I passed my 312-50 exam just recently. I recommend to anybody who wants to pass in their 312-50 exam.
 Samantha
I got most of latest 312-50 dump questions in it.
 Janet
Pass4cram provided the latest, reliable 312-50 questions dump, it worked well with me. I passed the exam successfully. Thanks!
 Nathaniel
I not only passed my exam with 89% marks but also got salary enhancement from my BOSS. Thank you very much. Good exam dump!!!
 Lawrence
This is still valid. Passed today with 80%. looked like 3-4 new questions. Many thanks! Good braindumps
 Horace

Pass4cram Practice Exams are written to the highest standards of technical accuracy, using only certified subject matter experts and published authors for development - no all vce.

We are committed to the process of vendor and third party approvals. We believe professionals and executives alike deserve the confidence of quality coverage these authorizations provide.

If you prepare for the exams using our Pass4cram testing engine, It is easy to succeed for all certifications in the first attempt. You don't have to deal with all dumps or any free torrent / rapidshare all stuff.

Pass4cram offers free demo of each product. You can check out the interface, question quality and usability of our practice exams before you decide to buy.
The most valid exam cram is the best study and review material for your upcoming IT exam. With the useful and accurate pass4cram study material, you will pass your exam with a high core.
Copyright © 2026 Pass4cram NETWORK CO.,LIMITED. All Rights Reserved. All trademarks used are properties of their respective owners. Privacy Policy
