

I scored 98% marks in the 412-79v9 certification exam. I prepared with the exam practising software by Pass4cram. Made it very easy to take the actual exam. Highly suggested to all
 Viola


Exam Code: 412-79v9
Exam Name: EC-Council Certified Security Analyst (ECSA) v9
Updated: Oct 20, 2026
Q & A: 205 Questions and Answers
412-79v9 Free Demo download
What makes one set of practice materials more effective than another? Often it is the organization of the content. The EC-COUNCIL EC-Council Certified Security Analyst (ECSA) v9 question bank at Pass4cram is arranged so the important points surface early and clearly, letting you build a command of the 412-79v9 exam essentials in less time than unstructured review allows.
| Section | Objectives |
|---|---|
| Topic 1: Web Application Security Testing | - Web application attack vectors - SQL injection and XSS testing |
| Topic 2: Network Scanning and Enumeration | - Network enumeration techniques - Port scanning and service detection |
| Topic 3: System Hacking and Privilege Escalation | - Privilege escalation methods - Password cracking techniques |
| Topic 4: Penetration Testing Reporting | - Documentation of findings - Risk reporting and remediation guidance |
| Topic 5: Vulnerability Analysis | - Threat assessment and risk analysis - Vulnerability scanning tools and interpretation |
| Topic 6: Wireless Network Attacks | - Wireless attack techniques and mitigation - Wi-Fi security assessment |
| Topic 7: Reconnaissance and Footprinting | - OSINT techniques - Passive and active reconnaissance |
| Topic 8: Social Engineering | - Human vulnerability exploitation - Phishing and impersonation techniques |
| Topic 9: Penetration Testing Concepts & Methodology | - Ethical hacking frameworks and methodologies - Information security laws and compliance |
Recommended: Certified Ethical Hacker (CEH) or equivalent knowledge in penetration testing fundamentals
The 412-79v9 exam contains 150 questions with 240 minutes minutes on the clock. That combination rewards candidates who have rehearsed under realistic conditions — which is exactly what the software simulation version of the Pass4cram materials is for.
The official outline divides the 412-79v9 exam into weighted domains, including:
The EC-COUNCIL EC-Council Certified Security Analyst (ECSA) v9 question bank at Pass4cram is organized around these same objectives, and its clear layout makes the heavily weighted points easy to spot and revisit.
EC-COUNCIL provides these training resources for candidates:
Pair them with structured practice questions and simulation sessions, and you cover both the knowledge and the experience sides of exam preparation.
The passing score is 70% and the exam fee is $550 USD (approx.). A practical approach: keep running timed practice sets until your results sit comfortably above the passing line, then book your seat.
Because knowing the content and knowing the exam are different skills. The software version of the EC-COUNCIL EC-Council Certified Security Analyst (ECSA) v9 materials simulates the real 412-79v9 exam environment, so the interface, timing, and question flow are familiar before you sit the real thing. It is a small rehearsal with an outsized effect — candidates who have experienced the simulation handle exam-day details calmly instead of burning time on surprises.
Registration is handled through the official channels below:
Pick a date that leaves room for at least a few full simulation sessions — that final rehearsal window is where preparation consolidates.
The 412-79v9 exam is the official test for the EC-COUNCIL EC-Council Certified Security Analyst (ECSA) v9 certification from EC-COUNCIL, measuring how well you can apply the published exam objectives in realistic scenarios. The credential validates your skills against an industry-recognized standard — and because the exam has its own format and rhythm, materials that combine organized content with realistic simulation prepare you more completely than reading alone.
Three things. First, it starts with a free demo containing plenty of sample questions, so you can taste the 412-79v9 exam content before deciding. Second, the PDF prints cleanly, turning your screen materials into paper you can annotate — notes in the margins keep your memory of key points fresh every time you pick the pages back up. Third, it travels anywhere: no account login, no compatibility worries, just 205 practice questions for the EC-COUNCIL EC-Council Certified Security Analyst (ECSA) v9 exam ready whenever you are.
Internet Control Message Protocol (ICMP) messages occur in many situations, such as whenever a datagram cannot reach the destination or the gateway does not have the buffering capacity to forward a datagram. Each ICMP message contains three fields: type, code, and checksum. Different types of Internet Control Message Protocols (ICMPs) are identified by a type and code field.
Which of the following ICMP messages will be generated if the destination port is not reachable?
Correct Answer: A 🗳️
A Blind SQL injection is a type of SQL Injection attack that asks the database true or false questions and determines the answer based on the application response. This attack is often used when the web application is configured to show generic error messages, but has not mitigated the code that is vulnerable to SQL injection.
It is performed when an error message is not received from application while trying to exploit SQL vulnerabilities. The developer's specific message is displayed instead of an error message. So it is quite difficult to find SQL vulnerability in such cases.
A pen tester is trying to extract the database name by using a blind SQL injection. He tests the database using the below query and finally finds the database name.
http://juggyboy.com/page.aspx?id=1; IF (LEN(DB_NAME())=4) WAITFOR DELAY
'00:00:10'--
http://juggyboy.com/page.aspx?id=1; IF (ASCII(lower(substring((DB_NAME()),1,1)))=97)
WAITFOR DELAY '00:00:10'--
http://juggyboy.com/page.aspx?id=1; IF (ASCII(lower(substring((DB_NAME()),2,1)))=98)
WAITFOR DELAY '00:00:10'--
http://juggyboy.com/page.aspx?id=1; IF (ASCII(lower(substring((DB_NAME()),3,1)))=99)
WAITFOR DELAY '00:00:10'--
http://juggyboy.com/page.aspx?id=1; IF (ASCII(lower(substring((DB_NAME()),4,1)))=100)
WAITFOR DELAY '00:00:10'--
What is the database name?
Correct Answer: A 🗳️
Explanation: Only visible for Pass4cram members. You can sign-up / login (it's free).
Which of the following protocol's traffic is captured by using the filter tcp.port==3389 in the
Wireshark tool?
Correct Answer: C 🗳️
Explanation: Only visible for Pass4cram members. You can sign-up / login (it's free).
Which one of the following tools of trade is an automated, comprehensive penetration testing product for assessing the specific information security threats to an organization?
Correct Answer: C 🗳️
SQL injection attacks are becoming significantly more popular amongst hackers and there has been an estimated 69 percent increase of this attack type.
This exploit is used to great effect by the hacking community since it is the primary way to steal sensitive data from web applications. It takes advantage of non-validated input vulnerabilities to pass SQL commands through a web application for execution by a back- end database.
The below diagram shows how attackers launched SQL injection attacks on web applications.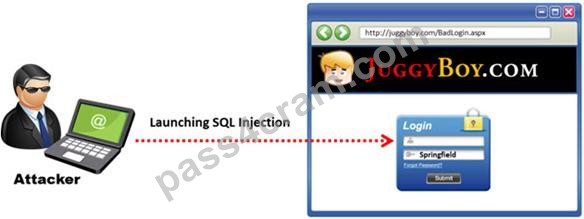
Which of the following can the attacker use to launch an SQL injection attack?
Correct Answer: C 🗳️
Viewing page 1 out of 41 pages.
Viewing questions 1-5 out of 205 questions.

Pass4cram confidently stands behind all its offerings by giving Unconditional "No help, Full refund" Guarantee. Since the time our operations started we have never seen people report failure in the 412-79v9 exam after using our products. With this feedback we can assure you of the benefits that you will get from our products and the high probability of clearing the EC-COUNCIL 412-79v9 exam.
We still understand the effort, time, and money you will invest in preparing for your certification exam, which makes failure in the 412-79v9 exam really painful and disappointing. Although we cannot reduce your pain and disappointment but we can certainly share with you the financial loss.
This means that if due to any reason you are not able to pass theactual 412-79v9 exam even after using our product, we will reimburse the full amount you spent on our products. you just need to mail us your score report along with your account information to address listed below within 7 days after your unqualified certificate came out.
Over 28240+ Satisfied Customers
I scored 98% marks in the 412-79v9 certification exam. I prepared with the exam practising software by Pass4cram. Made it very easy to take the actual exam. Highly suggested to all
Viola
Found the latest exam dumps for ECSA certification exam at Pass4cram. I couldn't clear my exam last time because the questions were different from what i studied. Now I got 96% marks. Thank you Pass4cram for this amazing work.
 Denise

Carefully studied the 412-79v9 exam dumps and the questions are almost all from the 412-79v9 exam dump,I got the 412-79v9 certification without difficulty.
 Enoch
You can pass the 412-79v9 exam easily with this 412-79v9 training dump. This is the best 412-79v9 study material i’ve found. Great!
 Alfred
I passed the 412-79v9 exam only using these 412-79v9 practice questions! They are great. You should buy and pass with them as well.
 Aurora
I believe that every candidate who use 412-79v9 dump will not regret. I passed my 412-79v9 exams today. Reallt great!
 Josephine

412-79v9 exam is not easy but this Pass4cram has helped me understand what is needed. Thank you!!!
 Jacob
I recently took and passed the 412-79v9 exams by using Pass4cram 412-79v9 exam dump. If you have it, you should do well on your EC-COUNCIL exams.
 Poppy
Updated dumps for 412-79v9 certification at Pass4cram. Older versions aren't as beneficial as the latest ones. Passed my exam 2 days ago with 90% marks. Thank you Pass4cram.
 Alberta
I'm so happy that I passed 412-79v9 exam a week ago.
 Franklin
I just want to let you know I passed my 412-79v9 exam today. Your 412-79v9 exam questions closely matched the actual 412-79v9 exam.
 Penelope
Hi, I passed the 412-79v9 exam with these helpful 412-79v9 exam dumps. Thanks a lot!
 Sheila
Just to inform you that I had passed the 412-79v9 exam with 90% full mark. Thanks for your 412-79v9 practice exam! Terrific!
 Mark
Scored 100% on this 412-79v9 exam.
 Madge
I am afraid to spend time for nothing so i bought this 412-79v9 exam file to attend the exam. Now i have gotten the certification. Yes, i am a positive man!
 Jane

Pass4cram Practice Exams are written to the highest standards of technical accuracy, using only certified subject matter experts and published authors for development - no all vce.

We are committed to the process of vendor and third party approvals. We believe professionals and executives alike deserve the confidence of quality coverage these authorizations provide.

If you prepare for the exams using our Pass4cram testing engine, It is easy to succeed for all certifications in the first attempt. You don't have to deal with all dumps or any free torrent / rapidshare all stuff.

Pass4cram offers free demo of each product. You can check out the interface, question quality and usability of our practice exams before you decide to buy.
The most valid exam cram is the best study and review material for your upcoming IT exam. With the useful and accurate pass4cram study material, you will pass your exam with a high core.
Copyright © 2026 Pass4cram NETWORK CO.,LIMITED. All Rights Reserved. All trademarks used are properties of their respective owners. Privacy Policy
